Me Impact Research
tamimping@gmail.com linkedin.com/in/tamimping
Tamim Ibne Shahidullah

Hi, I’m Tamim Ibne Shahidullah.

Application Security Engineer

I am an Application Security Engineer with 7 years of experience. I mainly focus on securing web/mobile applications and APIs, while also reviewing source code and cloud environments. I use my programming background to build custom automation tools, and I combine deep manual testing with AI to find complex bugs.


In my spare time, I do vulnerability research to keep my skills sharp. I work with large organizations to help them identify and patch their security flaws. My vulnerability reports have been rewarded by major companies like OpenAI, BMW, and Coca-Cola.
Rewarded By Industry Leaders

OpenAI
OpenAI
BMW
BMW
Coca-Cola
Coca-Cola
Canva
Canva
Indeed
Indeed
Basecamp
Basecamp
HubSpot
HubSpot
Priceline
Priceline
Rockstar Games
Rockstar Games
Disney
Disney+
Sony
Sony
Expedia Group
Expedia Group
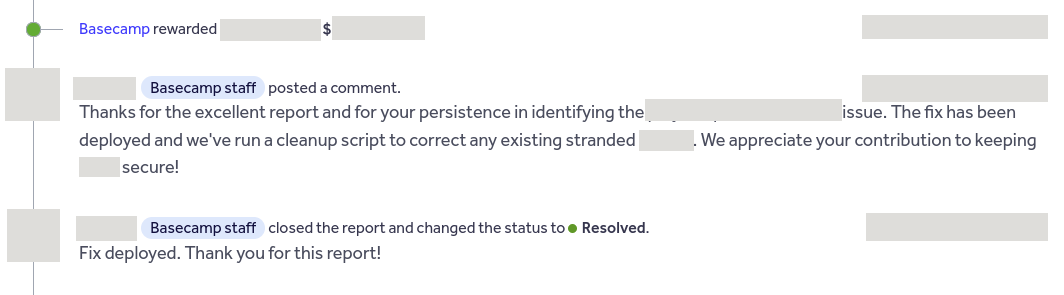
Screenshot
šŸ” Click to expand
Rewarded by Basecamp
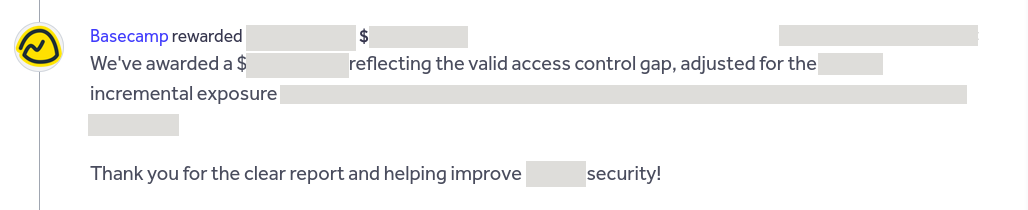
Screenshot
šŸ” Click to expand
Rewarded by Basecamp
Screenshot
šŸ” Click to expand
Rewarded by Baidu
Screenshot
šŸ” Click to expand
Rewarded by Rockstar Games
Screenshot
šŸ” Click to expand
Rewarded by OpenAI
Screenshot
šŸ” Click to expand
Rewarded by Lyst

Security Research

Cross-Tenant Auth Bypass

Exploiting shared database logic to bypass tenant boundaries, chained with a CSRF to destroy enterprise API keys.

Read Full Article →

RBAC Bypass via Event Logs

Bypassing RBAC to leak sensitive restricted workspace data by exploiting separated event logs.

Read Full Article →

Persistent Webhook IDOR

Exploiting an API-level IDOR to maintain persistent access and disable webhooks after UI permissions were revoked

Read Full Article →
Me Impact Research
tamimping@gmail.com linkedin.com/in/tamimping