Hi, I’m Tamim Ibne Shahidullah.
Application Security Engineer
I am an Application Security Engineer with 7 years of experience. I mainly focus on securing web/mobile applications and APIs, while also reviewing source code and cloud environments. I use my programming background to build custom automation tools, and I combine deep manual testing with AI to find complex bugs.
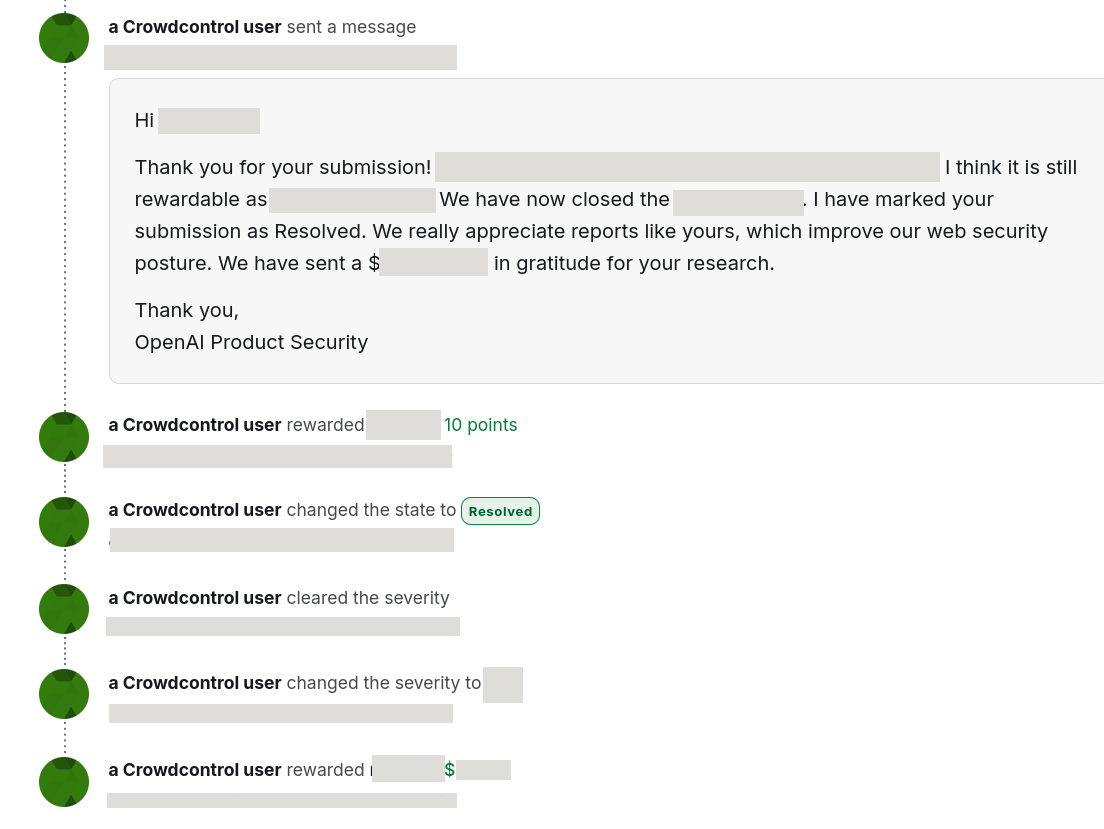
In my spare time, I do vulnerability research to keep my skills sharp. I work with large organizations to help them identify and patch their security flaws. My vulnerability reports have been rewarded by major companies like OpenAI, BMW, and Coca-Cola.